OAM as IDP and SP (2 OAM PS3)

Oracle Access Manager can act as Identity Provider or Service Provider based on requirement.I configured a use case where one OAM is acting as IDP and another one acting as SP. High level steps  are as below: 

Download the IDP OAM metadata by accessing the below URL:

http://<IDP-OAM>:14100/oamfed/sp/metadata

Note that metadata consists both IDP and SP in one file. While importing IDP metadata remove SP metadata from the file.

Login to the SP OAM console and click on federation. Click on Service Provider Management.
Import the Idp metadata.
Click ‘Create Authentication Scheme and Module’ to create the scheme and module.


Now Login to Idp VM and import the Service provide metadata.
Remember to modify the metadata to contain only Service Provider metadata.

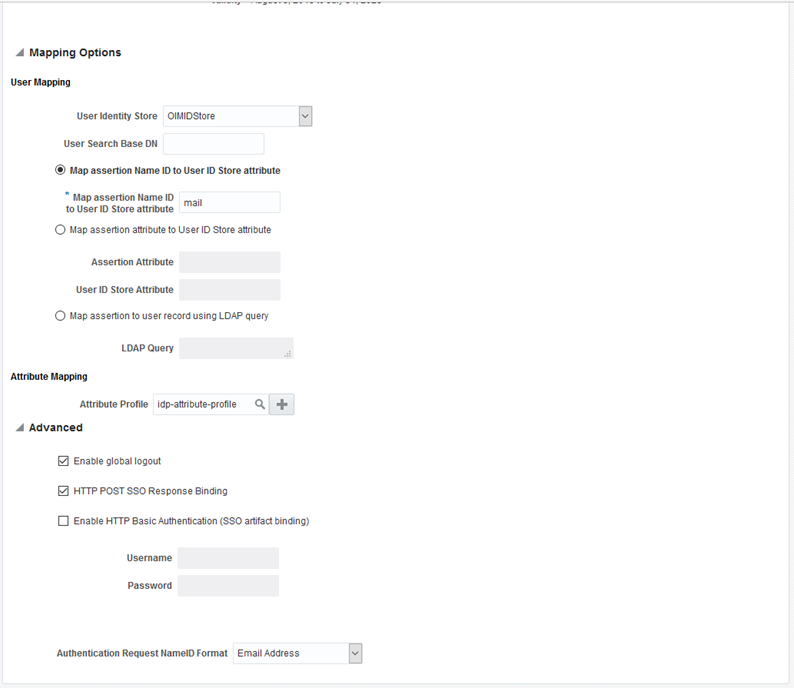
Provide the NameID Value as mail.


Access any application protected by SP OAM and it will redirect to the IDP -OAM.


Comments

  1. Thanks for sharing the valuable post.
    I have a requirement where I have to make my OAM as both(IDP and SP) at a time
    ERP(SP)<==>OAM(IDP)==OAM(SP)<==>MS Azure(IDP)

    How to configure this? could you help please.

    If possible please provide the solution in my email "ravcusat23@gmail.com"
    Thanks,
    Ravi Ranjan

    ReplyDelete

Post a Comment

Popular posts from this blog

Adding UDF (User Defined Field) on create user page OIM 11g R2 PS1:-

    Login to Sysadmin console and create a Sandbox and activate it. Click on Form Designer and search for user form. 2.      Create a new field of desired type. 3.      Provide the Required Values for UDF creation and click save and close. UDF field will be added then publish the sand box. 4.      Login to Identity console now and create another sandbox and activate it. After sandbox is activated click on users link and the click on create user. 5.      Provide the mandatory values on the form and then click the customize button on top. Select source from the view. 6.      Select the panel where the field has to be added. Select panel form lay out click add content. Select Data component Catalog from the box. 7.      Select UserVO from the bottom. ...

Oracle Identity Cloud Service (IDCS)

   Oracle Identity Cloud Service i s the next generation comprehensive security and identity platform that is cloud-native and designed to be an integral part of the enterprise security fabric, providing modern identity for modern applications.  IDCS is a cloud-based identity management system that works by associating specific rights and restrictions with each user’s established identity. User provisioning, access control, and directory services are critical components of Oracle’s cloud-based security portfolio. Oracle Identity Cloud Service has been designed to meet the needs of organizations in a number of typical use-case scenarios, such as the cloud (allowing both on-premise and cloud resources to be secured from a single set of controls), mobile access (providing sign on for native or browser-based apps), employee-facing intranet and customer-facing extranet solutions.  Key Features: Oracle Identity Cloud Service provides the following functionali...

What is CASB - Oracle CASB Cloud Service

What is CASB: Cloud Access Security Brokers is a term coined by Gartner to describe cloud solutions centered around these four main pillars: visibility, compliance, data security, and threat protection. As per Gartner  Cloud access security brokers (CASBs)  are on-premises, or cloud-based security policy enforcement points, placed between cloud service consumers and cloud service providers to combine and interject enterprise security policies as the cloud-based resources are accessed. CASBs consolidate multiple types of security policy enforcement. Example security policies include authentication, single sign-on, authorization, credential mapping, device profiling, encryption, tokenization, logging, alerting, malware detection/prevention and so on.   To Summarize CASB is a service which is used to secure and monitor Cloud and On-Prem applications and to respond with remediation in case of Threats or suspicious events are detected. Key is the analysis of events ge...